 RuleExpert
Free DPDP compliance score
Your DPDP score in 5 minutes. No login. No card.
Answer questions about how your organisation actually works and get a score, your penalty exposure in rupees, and a ranked list of what to fix.
Check your DPDP score — free See how it is scored Free, always. No account, no expiring trial, no sales call.
5 minutes start to score 11 dimensions scored separately Exposure in ₹, not in jargon
You do not know where you stand
That is the normal starting point, and it is worth five minutes to replace it with a number.
You are not sure a clinic your size is even in scope, and nobody has told you otherwise.
A customer asked for your compliance posture and you had nothing to send back.
You handle three different groups of people’s data and have never separated what you owe each one.
What you get
Four things, before you pay anything
Not a lead-capture quiz with the answer behind a form. The assessment is the product, and this much of it is free.
01
A score out of 100
Eleven dimensions of the Act scored separately and weighted, then a single number and a risk band you can put in front of a board.
02
Your exposure in rupees
A penalty range built from the Act’s Schedule — every section you fall short on, weighted by how far short you are.
03
Your three biggest gaps
Ranked by what they cost you, not by what is easiest to fix. Ties broken by the larger penalty, so the expensive thing surfaces first.
04
A phased plan
The gaps turned into a 0–30, 30–90 and 90+ day roadmap, so your first week has something concrete in it.
How the score is built
Not a checklist. A weighted model.
A DPDP compliance checklist counts ticks. This DPDP assessment weights each gap by what the Act penalises.
1
Questions that fit your sector
Between 33 and 43 questions depending on your industry and whether children’s data or Significant Data Fiduciary duties apply. A hospital is asked about clinical records; a logistics operator is not. Each answer scores on a five-point scale, not yes/no — because “we have a policy nobody follows” is not the same as “we have none”.
2
Eleven dimensions, weighted
Data mapping, security, notice, consent, rights, breach, retention, vendors, grievance redressal, cross-border transfer and governance — plus children’s data and SDF duties where they apply. Weights shift if you are a Data Processor rather than a Data Fiduciary, because your obligations differ.
3
A dependency cap that stops a flattering score
If your data mapping or your security scores below 30%, the total is capped at 50 however well everything else scored. Below 30% on both, it is capped at 35. You cannot honour a rights request for data you cannot find, so a high score on top of a blank map would be a lie.
4
Exposure priced from the Act’s Schedule
Each gap is multiplied by the maximum penalty the Schedule sets for that obligation — ₹250 Cr for a security failure, ₹200 Cr for breach reporting or children’s data, ₹150 Cr for Significant Data Fiduciary duties, ₹50 Cr for most others — and scaled by how far short you fall.
Indicative only. Penalties are set by the Data Protection Board at its discretion, and are assessed per contravention rather than capped at a single figure.
The result
A number your CFO understands
“Section 6 non-conformance” does not get budget. A rupee figure against a named obligation does.
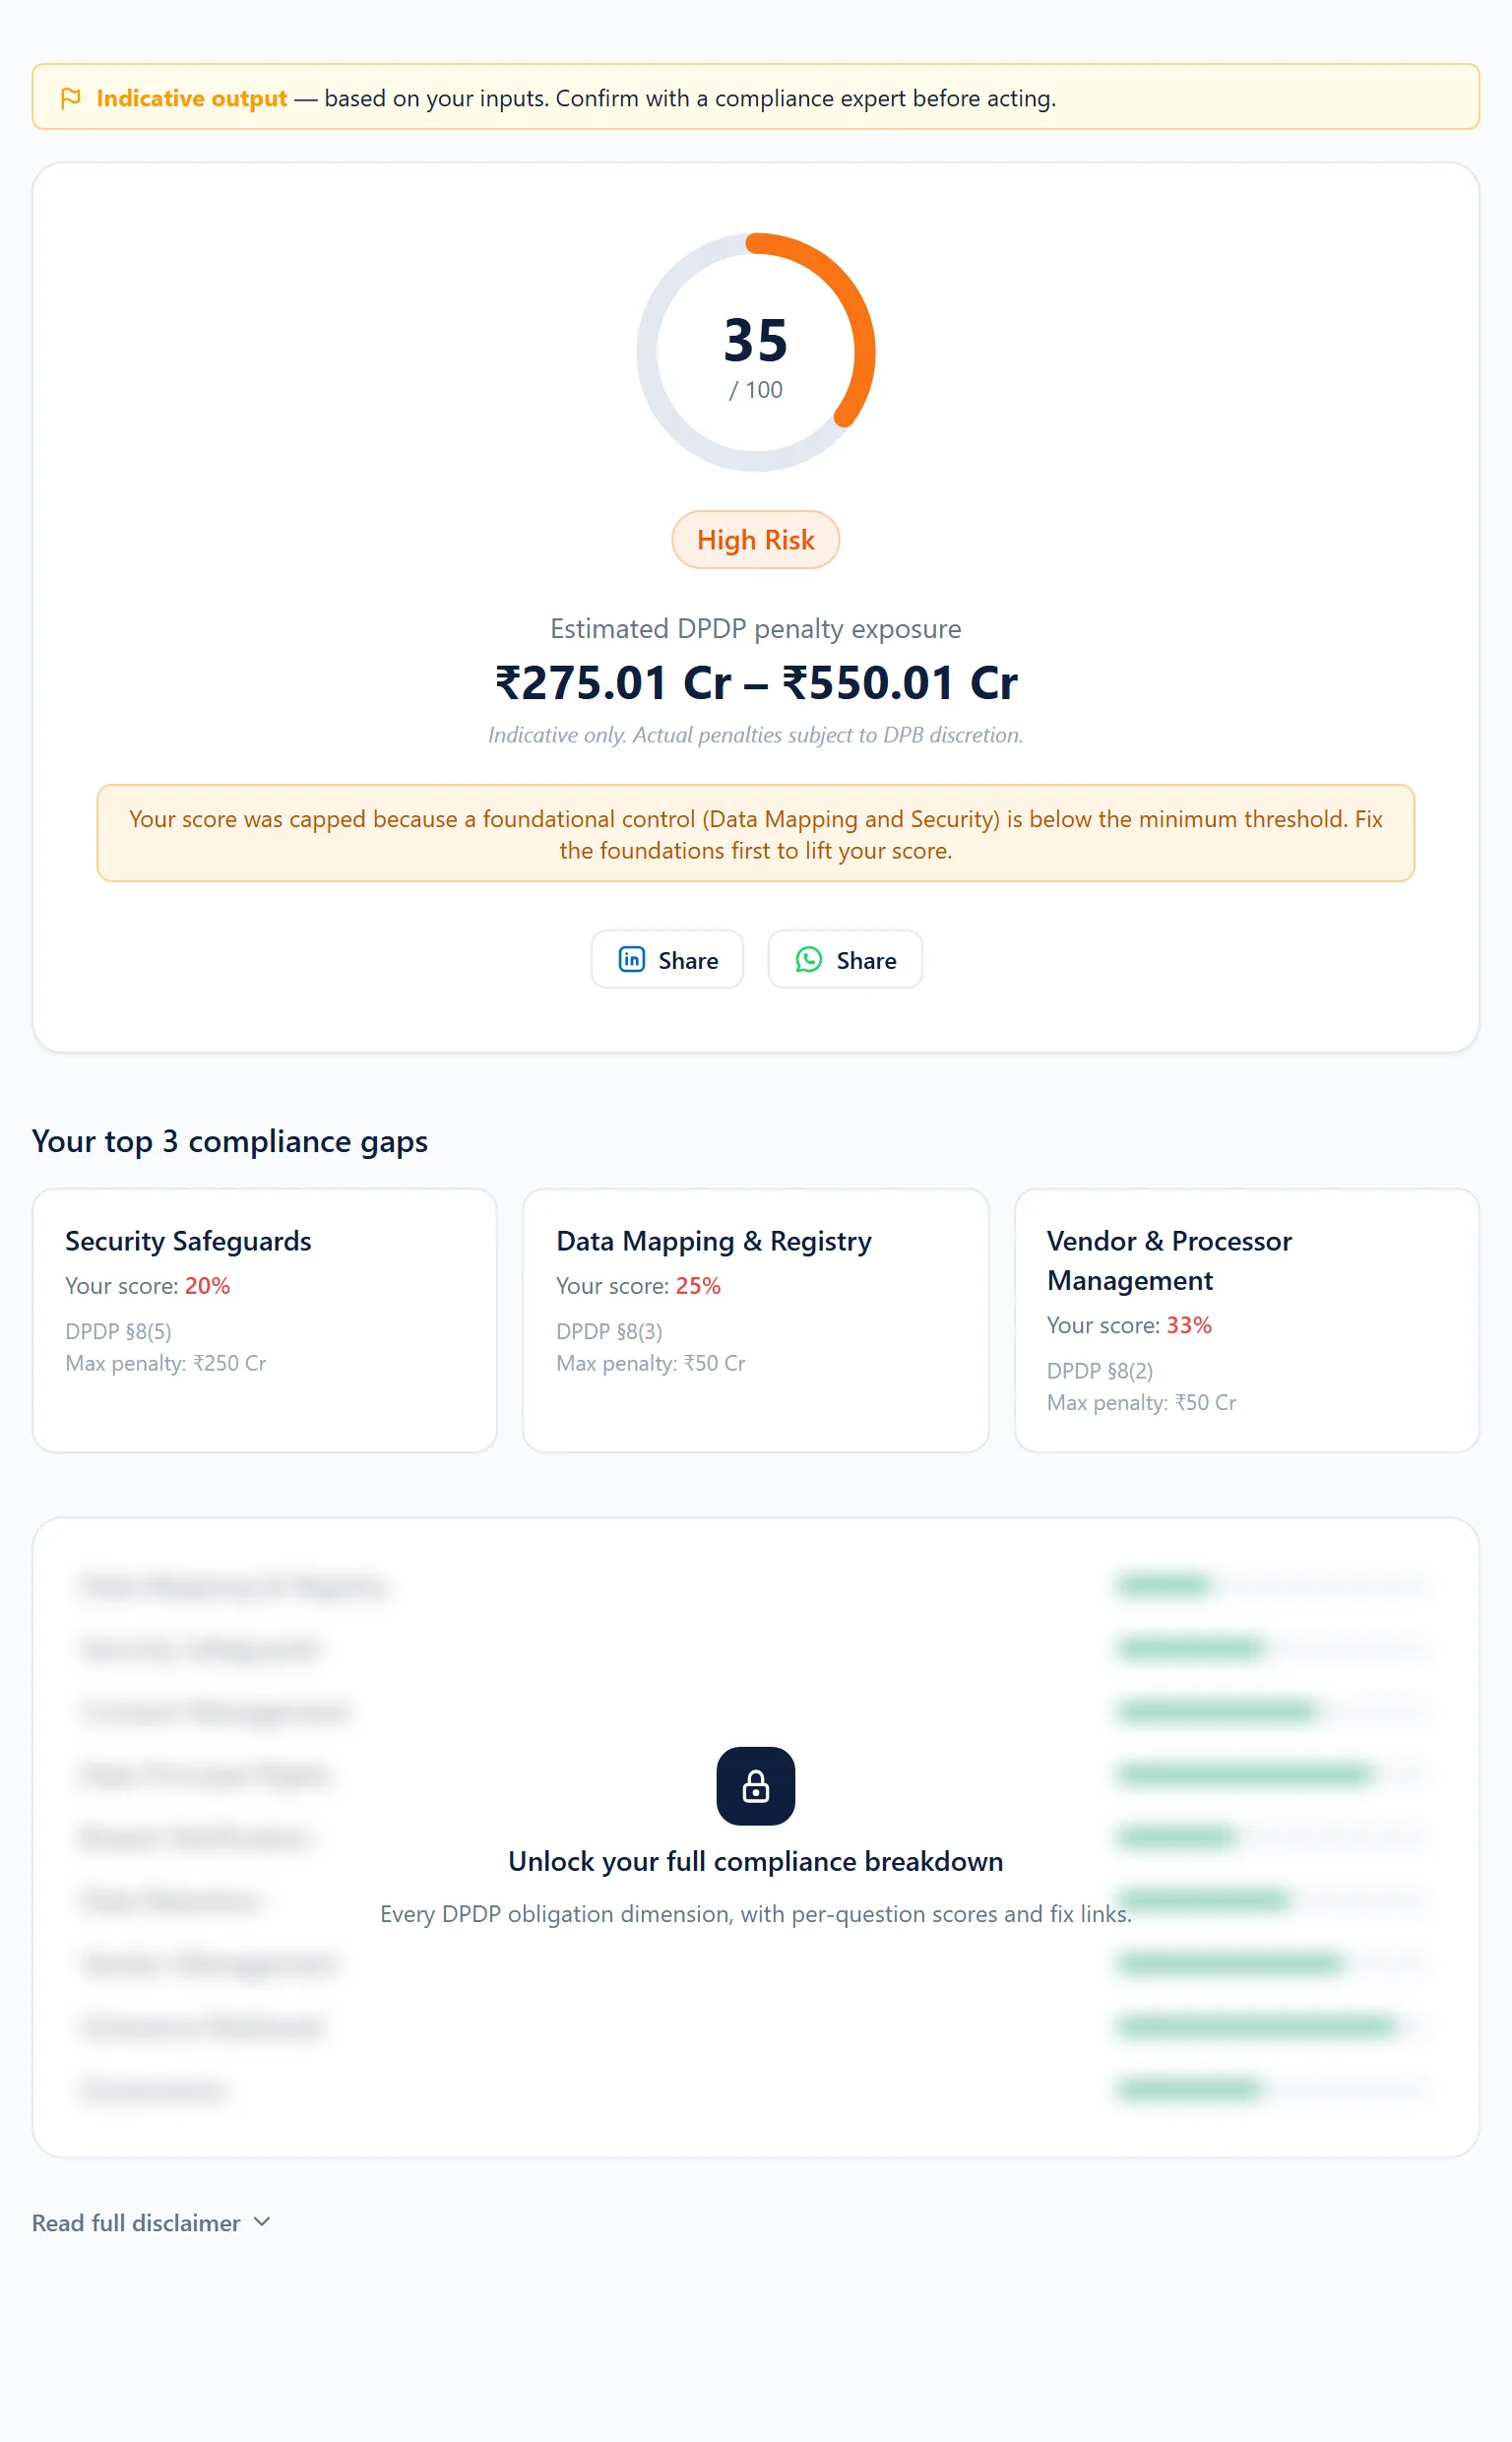
0–25Critical Core obligations largely unmet. Exposure across most of the Schedule.
26–45High risk Something exists on paper. Little of it is operating or evidenced.
46–65Moderate Consent and notice are moving. Rights, breach and vendors usually are not.
66–80Low risk A working programme with named gaps rather than unknown ones.
81–100Strong Obligations met and evidenced. The work is now keeping it true.
What costs money
Where the free part ends
Everything you need to know where you stand is free. The written report is what you buy, and only if you want it.
Free, no account
- Your score out of 100 and your risk band
- Penalty exposure as a rupee range
- Your three highest-cost gaps, ranked
- A 0–30 / 30–90 / 90+ day DPDP implementation plan
- A gap analysis of the data you described, gap by gap
- Re-score whenever you like, with the history kept
The full report
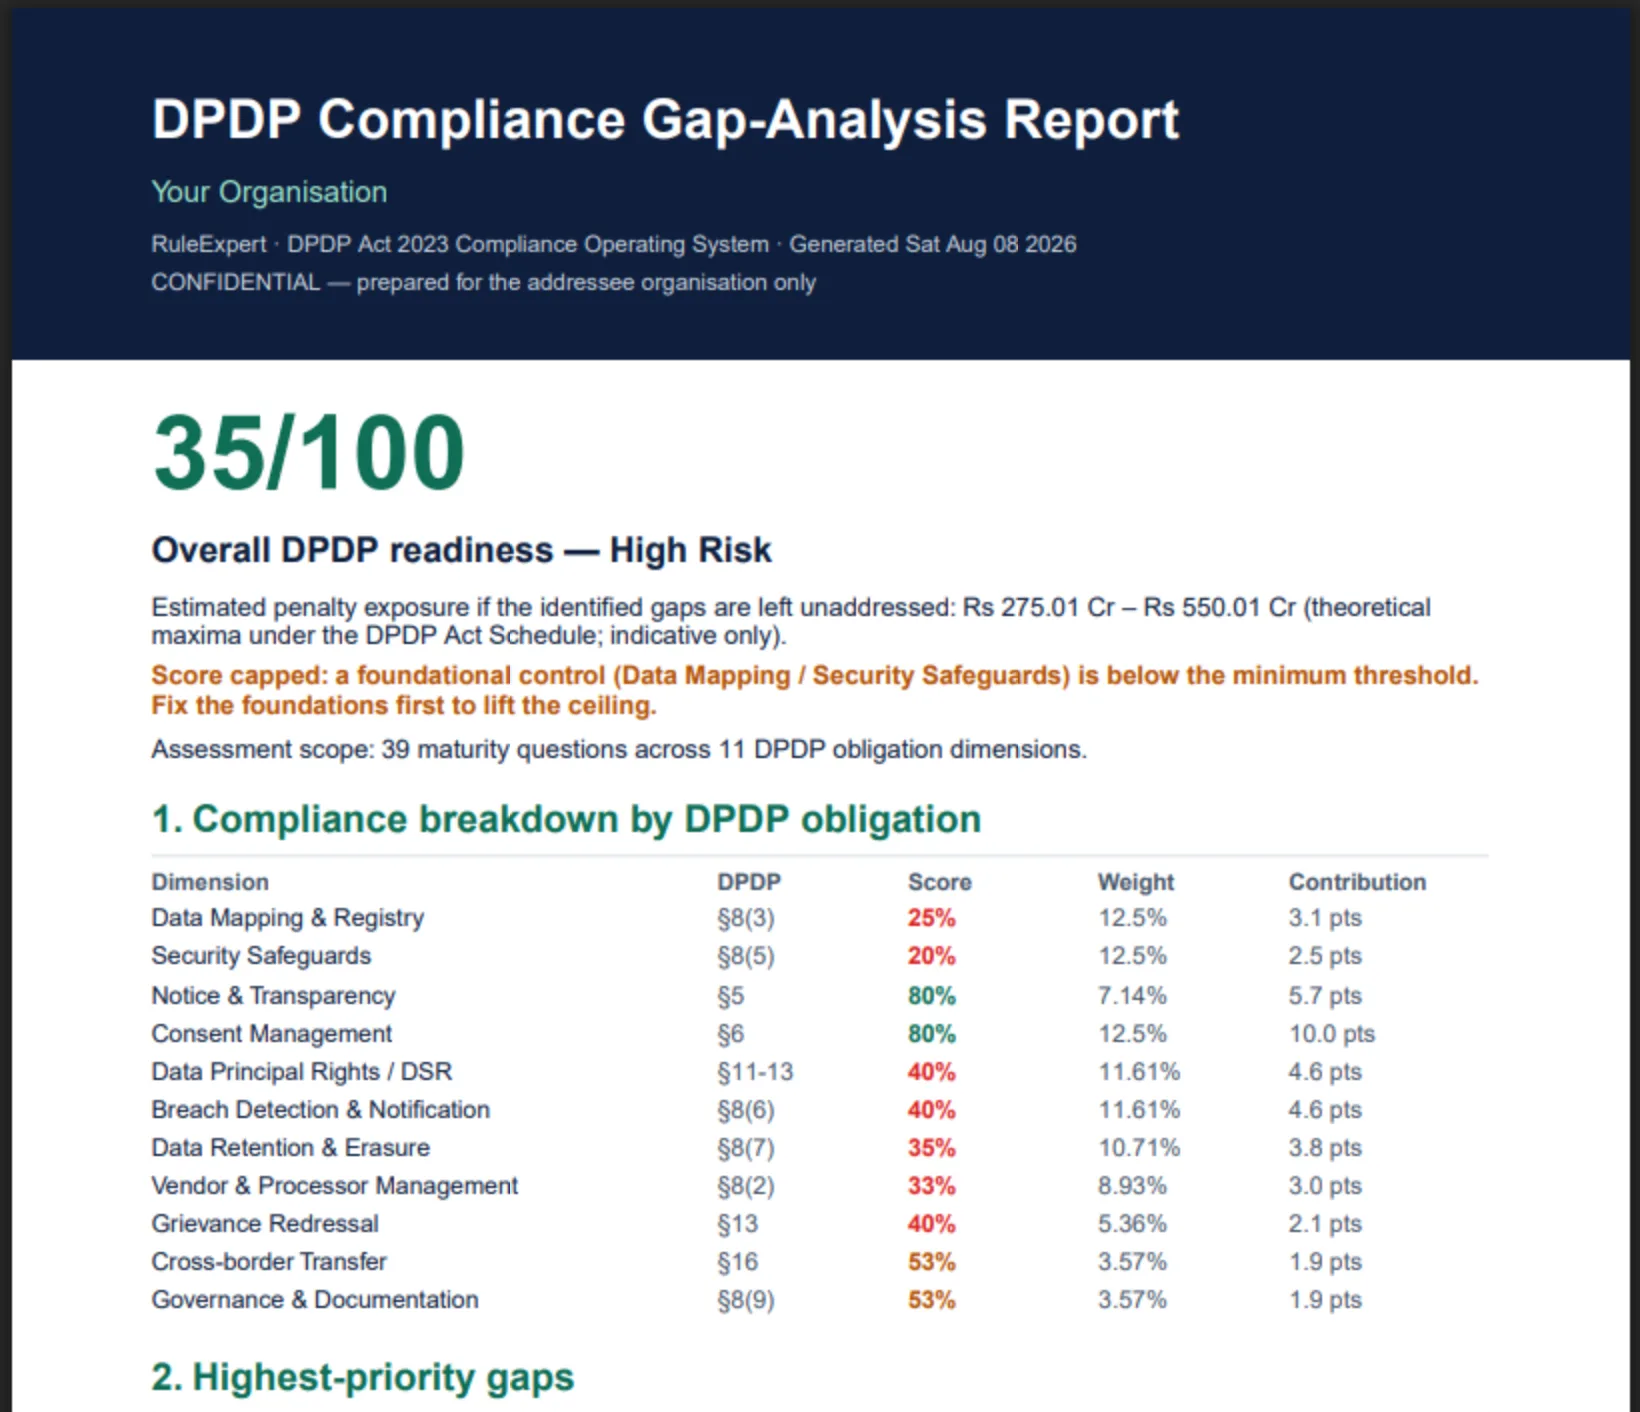
- All eleven dimension scores, with weights and contribution
- Every gap, not the top three
- A per-question annexure showing how each score was reached
- A written PDF for your board, DPO or counsel
One-off. No subscription, and no account needed to take the free assessment first.
Five minutes is less than this page takes to read.
No login, no card, no sales call. You get the score, the exposure and the plan whether or not you ever talk to us.
How it works
Three steps to a score
The only thing we ask for before the result is an email, and only so the score is yours to come back to.
01 — ABOUT YOU
Your industry and role
Sector, and whether you act as a Data Fiduciary, a Data Processor, or both. This decides which questions you are asked and how the weights are set.
02 — THE QUESTIONS
33 to 43 questions
How your organisation actually works, one question at a time, on a five-point scale. Your answers save as you go, so you can stop and come back.
03 — THE RESULT
Score, exposure, plan
Verify your email and the result is on screen — score, risk band, rupee exposure, your three biggest gaps and the phased plan.
Built for one law
Scored against the Act, not a GDPR checklist
Most DPDP readiness tools are GDPR questionnaires with the country name swapped. Every question here maps to a section of the Act.
§
Every question cites its section
Notice under §5 and Rule 3, consent under §6, children under §9, security under §8(5), breach under §8(6) and Rule 7, rights under §11–14. You can check our working.
₹
Priced by India’s Schedule
Exposure comes from the penalties the DPDP Act actually sets, not from GDPR’s 4% of turnover. Different law, different arithmetic.
↻
Meant to be retaken
Fix something, re-score, and watch the number move. The history is kept, so improvement is visible rather than asserted.
Questions
About the scorecard
Is the DPDP Scorecard really free?
Yes. The score, your risk band, your penalty exposure in rupees, your three highest-cost gaps and the phased remediation plan are all free, with no account, no expiring trial and no sales call. The only thing you pay for is the full written report — every dimension broken out, every gap rather than the top three, and a PDF you can hand to a board. You never have to buy it to find out where you stand.
How long does it take?
About five minutes. You answer between 33 and 43 questions depending on your industry and whether children’s data or Significant Data Fiduciary duties apply. Answers save as you go, so you can stop and pick it up later without losing anything.
How accurate is a self-assessment?
It is as accurate as your answers, and we say so on the result itself — every score carries an “indicative” marker. What it is not is a guess: the weights come from what the Act penalises, the exposure comes from the Schedule, and a dependency rule caps the total if your data mapping or security is weak, so you cannot get a flattering score on top of a blank map. It tells you where to look and what it costs. Confirming it is what an audit is for.
Do I need to know our systems in detail?
No. The questions are about how your organisation works — who handles personal data, what you tell people, what happens when someone asks for their data back — not about database schemas. A DPO, a founder, a compliance lead or a CTO can all complete it. If you do not know an answer, that is itself a finding worth having.
What happens to my answers?
They are stored against your assessment so you can come back to your result and re-score later, and they sit on infrastructure in India. We ask for an email so the score is yours rather than a stranger’s, and we do not ask for anyone’s personal data — no customer records, no employee lists, nothing about the people you hold data about.
Why does my score have a cap on it?
If data mapping or security scores below 30%, the total is capped at 50 — below 30% on both, at 35 — however well the rest scored. It is deliberate. You cannot honour a rights request for data you cannot find, and you cannot secure what you have not mapped, so a high score sitting on top of either would be misleading. The result tells you when the cap has been applied and why.
Does the penalty figure mean we will be fined that?
No, and we would not claim it. It is an exposure model: for each obligation you fall short on, the maximum the Act’s Schedule sets for that obligation, scaled by how far short you fall. Real penalties are set by the Data Protection Board at its discretion, are assessed per contravention, and take into account the nature of the breach and what you did about it. The number is for prioritising work, not for provisioning.
Can I retake it after we fix things?
Yes, and it is designed for that. Re-score whenever you like; the history is kept so the movement is visible. Most organisations run it once to find out where they stand, then again after the first thirty days of the plan.
What compliance teams tell us
Real client quotes, attributed by role and sector — we never name a client.
DPDP, explained properly
DPDP in India: The Complete Guide to Data Protection Compliance, DPDP Guidelines and Automated Compliance Management (2026)
3 September 2026 · 35 min read DPDP Act
Healthcare Vendor Governance Under India’s DPDP Act: The Complete 2026–27 Compliance Framework
27 August 2026 · 32 min read DPDP Act
DPDP vs GDPR Compliance Tool: What’s Actually Different, and What a Tool Needs to Handle Both
26 August 2026 · 34 min readWorking across
Find out where you stand.
Five minutes, no login, no card. You get the score, your exposure in rupees and the plan — whether or not you ever talk to us.
Check your DPDP score — free Book a demo Get a free consultation