 RuleExpert
Data mapping & registry
You cannot protect what you cannot find
Every other DPDP obligation assumes you know where personal data lives. This is the map the rest of the platform reads from.
Book a demo See what we never store Or check your DPDP score first — free, five minutes, no account.
Where does personal data actually live?
Not the systems you would list in a meeting — the ones you would remember on the third pass.
Eight systems, plus the paper case sheets at reception and the WhatsApp group the doctors use.
Production, the warehouse, the support tool, and the analytics vendor a growth engineer added.
The ATS, the payroll bureau, the background-check agency, and a spreadsheet on a recruiter’s laptop.
Why this comes first
Four obligations that fail without it
Data mapping is not paperwork you do for its own sake. Each of these needs an answer it can only get from an inventory.
§8(5)₹250 Cr
Keep personal data secure with reasonable safeguards. You cannot protect a system nobody has written down.
Data Registry
§8(6)₹200 Cr
Report a breach to the Board within 72 hours. The first question is which data was affected, and in what.
Breach
§11–§14₹50 Cr
Answer a rights request. Finding one person means knowing every system that could be holding them.
Rights
§8(7)₹50 Cr
Erase data once its purpose is served. Retention runs against a catalogue, or it does not run at all.
Retention
§16₹50 Cr
Know what leaves India. A transfer you have not recorded is one you cannot disclose in a notice.
Cross-border
The line we drew
We hold the map, never the territory
A data inventory that copies your data has doubled your exposure. This one holds metadata and nothing else.
01
What goes in
System names, table and column names, data types, who owns them, which category each holds and where it sits. The shape of your estate, not its contents.
02
What never goes in
No values. Not a name, not an email, not a row, not a sample. The endpoint that takes your schema rejects any field that is not a column name or a type.
03
Why it is enforced, not promised
A second check reads anything a person types into a note and refuses it if it looks like an email, a phone number, an Aadhaar or a PAN.
This matters commercially as well as legally. A registry holding copies of your records becomes a Data Fiduciary problem of its own — another system in scope, another breach surface, another thing to answer for. Ours cannot be, because there is nothing in it to lose.
The inventory
Three layers, one record
Systems hold categories. Activities describe why. The registry keeps all three joined so a question can be answered once.
1
Systems
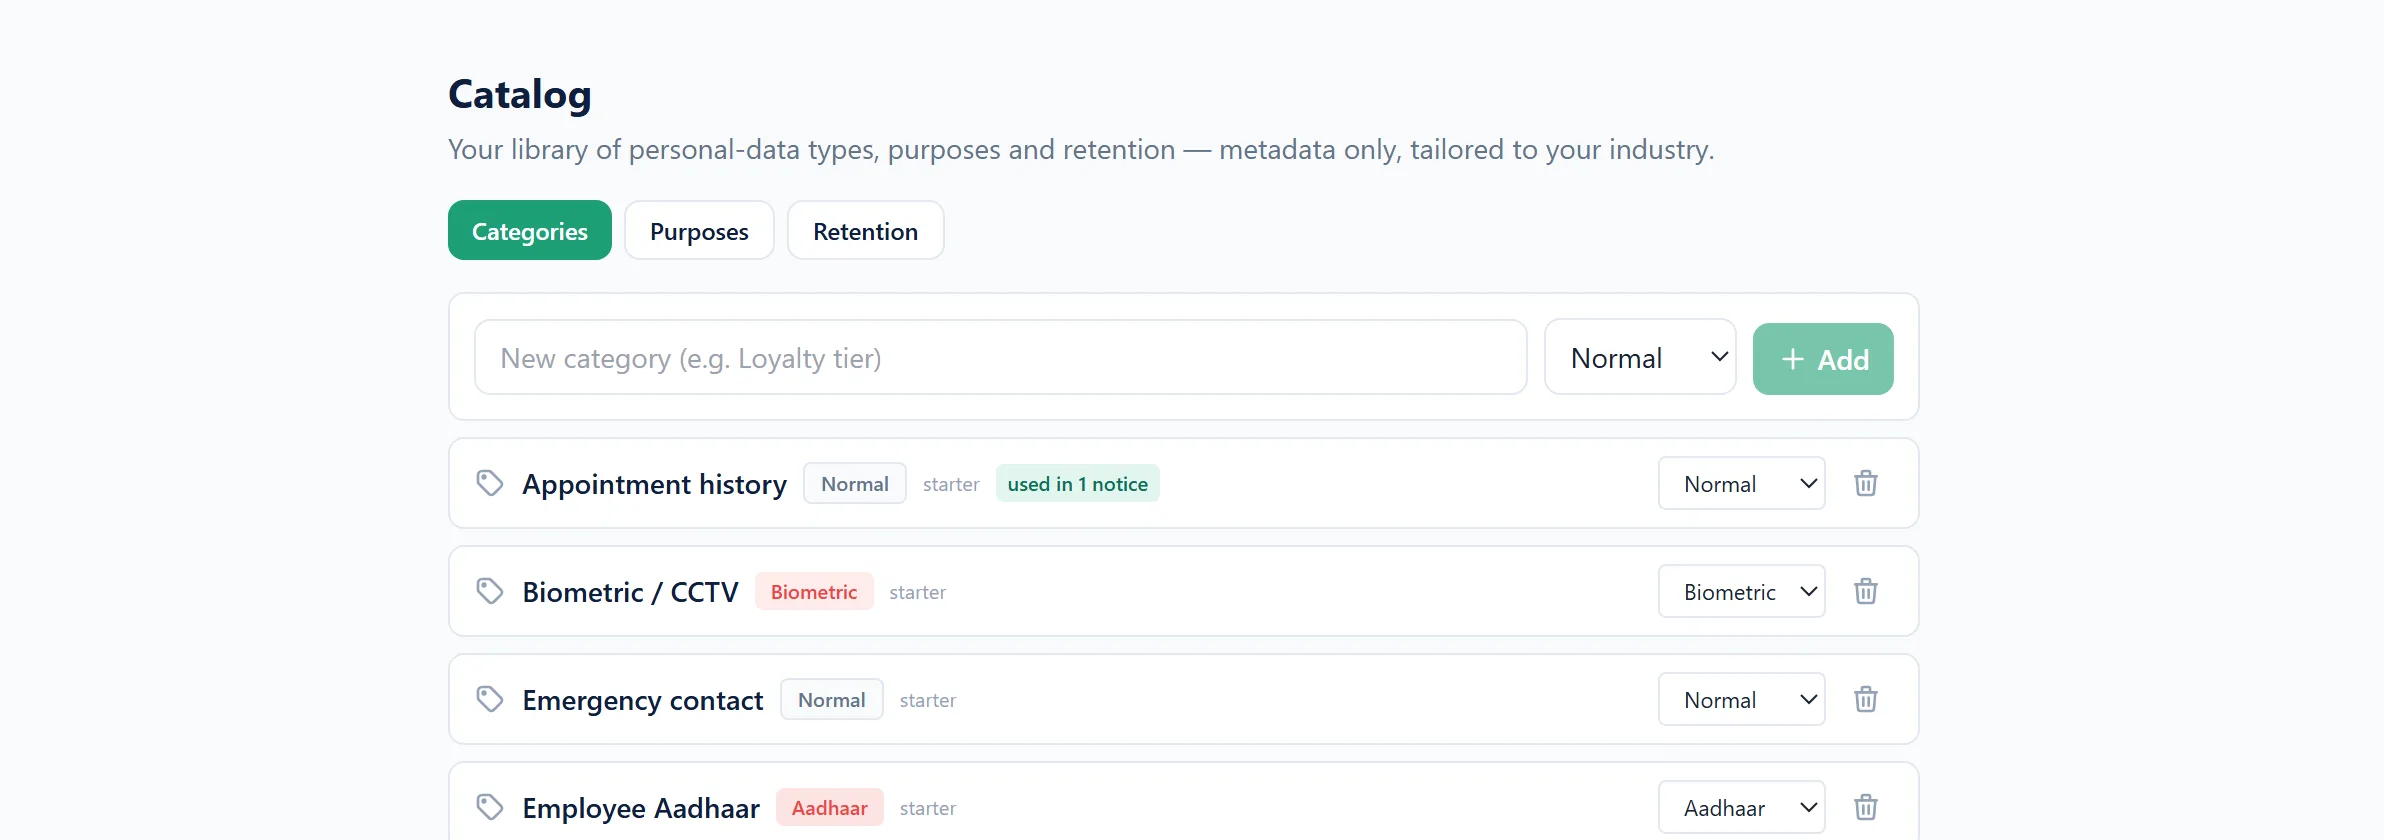
Everything that holds personal data, including the things nobody counts as a system — a shared drive, an agency’s spreadsheet, the register at reception. Each has an owner, a hosting location and a residency flag.
2
Categories
What kind of personal data each system holds, graded by sensitivity. Health records, financial details and children’s data carry weight the Act gives them, and that weight drives everything downstream.
3
Processing activities
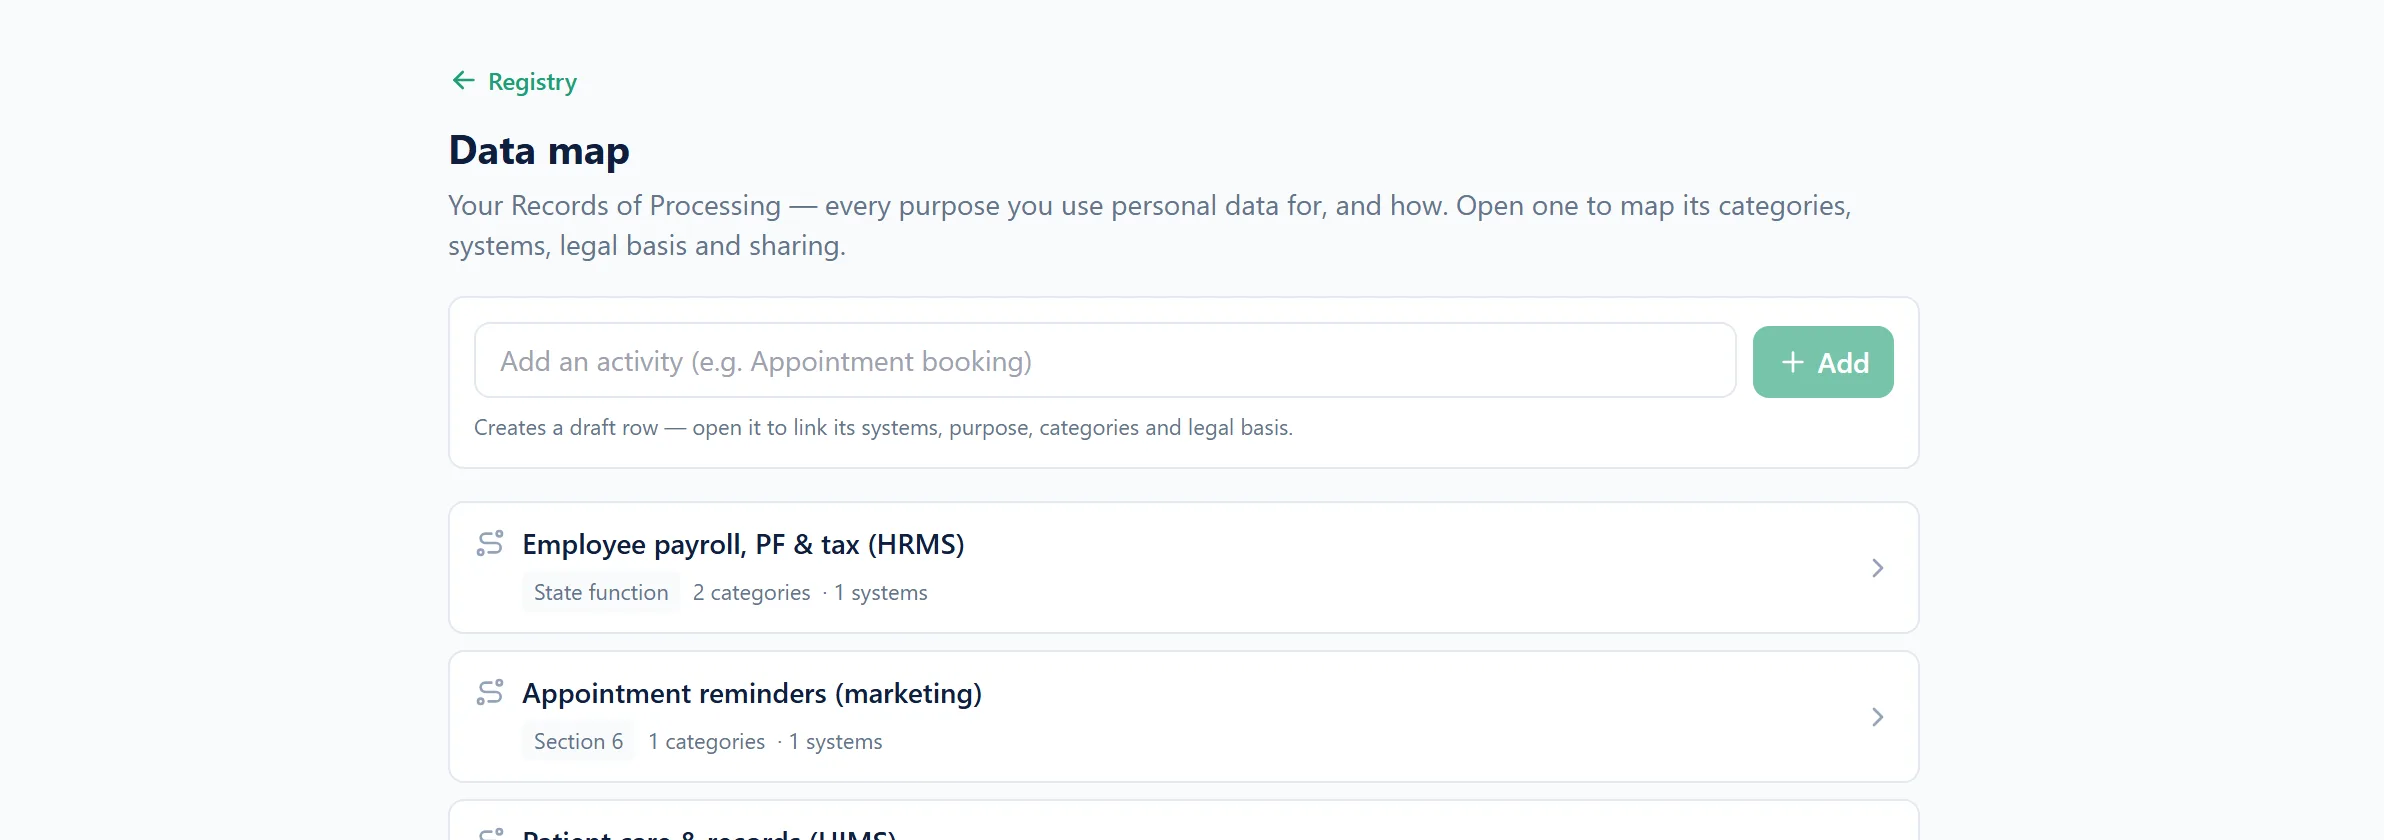
Why you hold it, on what basis, who it is shared with and for how long. This is the record of processing itself — not a document written once a year, but the thing the rest of the platform reads.
The objection
“Mapping our estate will take months”
It takes months when you start from an empty spreadsheet. You do not start from an empty spreadsheet.
01
Your sector arrives pre-filled
Pick your industry and the registry opens with the systems, categories and activities a business like yours actually runs. A hospital gets its clinical estate; a lender gets its own.
02
You confirm rather than compose
The work becomes correcting a draft — deleting what you do not have, adding what is missing, naming owners. Reviewing a list is a different job from writing one.
03
Paste a schema, get a classification
Export your table and column names and the rule library grades them by sensitivity. Every suggestion is reviewed one column at a time before it counts.
The assessment that makes the rest of it possible.
Our consultants read your documents, interview your people and walk your premises — and you keep the registry whether or not you buy anything else.
Risk
An inventory that ranks itself
A list of four hundred assets tells you nothing. The registry orders them by what the Act would actually penalise.
01
Weighted by sensitivity
A system holding children’s data or health records outranks one holding office contact details, because the Act treats them differently and so should your queue.
02
Gaps become findings
A system with no owner, a category with no lawful basis, personal data crossing a border with no notice clause — each surfaces as something to resolve, not a colour on a chart.
03
Resolved, with a reason
Closing a finding records who closed it and why. Accepting a risk deliberately is a defence; having never noticed it is not.
Downstream
Mapped once, used by everything
The registry is not a document that sits beside the platform. It is the thing the other modules read.
01
Consent knows what it covers
Each category is linked to the notice that authorises it, so a category with no lawful basis behind it is visible rather than assumed.
02
Rights requests fan out
A request becomes one task per system that could hold the person, because the registry already knows which systems those are.
03
Breach scoping starts answered
When an incident names a system, what it holds and who is affected is already recorded — on the clock that matters.
04
Retention runs per category
Erasure schedules attach to categories, so the clock is per kind of data rather than one blunt rule over everything.
05
Your score reflects reality
The data-mapping dimension of the DPDP Scorecard reads the registry directly instead of asking you to grade yourself.
Evidence
A record of processing, on demand
Built from what you maintain day to day, so producing it is an export rather than a project.
01
Assembled from the live registry
Systems, categories, activities, bases, recipients and retention — drawn from the records your team already keeps current, not typed again into a template.
02
Confirmed entries only
Anything still in draft or awaiting review is left out. A record of processing that includes guesses is worse than not having one.
03
Re-authentication before export
Downloading it needs your password again, and every export is written to an audit trail that cannot be edited afterwards.
§16 · Rule 15
What leaves India, and what that requires
No adequacy list to check — under the 2025 Rules transfer is permitted except where restricted.
01
Every system carries a location
Where it is hosted and whether that is inside India. A vendor console you signed up for in an afternoon is a transfer, and it counts.
02
Restricted destinations are flagged
The model is a blacklist, not an allow-list. Where the government restricts a country, the registry marks systems hosted there rather than leaving you to notice.
03
Notices are checked against it
A transfer abroad has to be disclosed. Where a system leaves India and the notice covering it says nothing, that mismatch is raised.
On the roadmap
What is coming, said plainly
Today the schema comes from you. Direct connectors are being built, and they will read structure only.
Direct database connectors
Coming soon
Read table and column names straight from your database instead of pasting an export. The same rule library, the same per-column review, no values read.
SaaS estate discovery
Coming soon
Surface the tools your teams signed up for without telling anyone, which is where most unmapped personal data actually sits.
Continuous re-scan
Coming soon
Notice when a new column appears in a system already mapped, so the registry keeps pace with your engineering team.
One thing will not change when those ship: none of them will read a value. Discovery works on names and types, because a compliance tool that copies your personal data has made your problem bigger.
Questions
About data mapping
Does the DPDP Act require a data inventory?
Not in those words, and that is the honest answer. No section says “maintain a data inventory”. What the Act does is impose duties that cannot be discharged without one — securing personal data under §8(5), reporting a breach within 72 hours under Rule 7, answering rights requests, erasing data when its purpose ends under §8(7). Every one of those begins with knowing what you hold and where. Significant Data Fiduciaries have the sharpest version of this, because Rule 13 requires an independent audit and an auditor asks for the inventory first.
Do you connect to our databases and read our data?
No, and the product is built so it cannot. The registry holds metadata — system names, table and column names, types, owners, categories, locations. The endpoint that accepts a schema rejects any field that is not a column name or a type, and a second check refuses free text that looks like an email, a phone number, an Aadhaar or a PAN. If you have been shown a data mapping tool that samples rows of your live data to detect personal information, ask where those samples are stored and who can read them.
How long does the first map actually take?
A working first pass in an afternoon for a single-location business, because the registry opens pre-filled for your sector rather than empty. Confirming and correcting a draft is a different task from composing one. Getting it genuinely complete — every shared drive, every agency, every spreadsheet somebody keeps locally — takes longer, and that is true of any method. We would rather say that than sell you a scan that claims to find things it cannot see.
What counts as a system?
Anything holding personal data, whatever it runs on. The hospital case makes the point: the registration counter’s paper case sheets are as much in scope as the hospital information system, and neither a scan nor a connector would ever find them. The Act does not care what the data is written on.
Can we export a record of processing?
Yes. It is assembled from the live registry rather than maintained separately, so it reflects what you actually hold on the day you export it. Only confirmed entries are included — drafts and unreviewed findings are left out. Export requires you to re-enter your password, and each one is written to an audit trail that cannot be edited.
Where does the registry itself live?
On infrastructure in India, along with everything else. Data at rest, backups included, stays in-country. And because the registry holds only metadata, the question carries less weight here than it would for a tool holding copies of your records.
What compliance teams tell us
Real client quotes, attributed by role and sector — we never name a client.
DPDP, explained properly
DPDP in India: The Complete Guide to Data Protection Compliance, DPDP Guidelines and Automated Compliance Management (2026)
3 September 2026 · 35 min read DPDP Act
Healthcare Vendor Governance Under India’s DPDP Act: The Complete 2026–27 Compliance Framework
27 August 2026 · 32 min read DPDP Act
DPDP vs GDPR Compliance Tool: What’s Actually Different, and What a Tool Needs to Handle Both
26 August 2026 · 34 min readWorking across
See an estate already mapped.
A registry with systems, categories and activities already in it — the risk queue, the cross-border flags, and a record of processing exported live.