 RuleExpert
Breach notification
You do not have 72 hours
Two of the three things you owe fall due the moment you find out. The 72 hours everyone quotes is only the third.
Book a demo See what the clock really looks like Or check your DPDP score first — free, five minutes, no account.
It has already happened. Now what?
None of these feels like a “data breach” at the time. Every one of them is one under Rule 7.
A laptop with discharge summaries goes missing from a doctor’s car.
A misconfigured storage bucket left customer records reachable for an unknown length of time.
A payroll file for one client was emailed to the wrong client, and they replied to say so.
Rule 7
Three duties, two clocks
Most summaries of a personal data breach under DPDP mention one deadline. The notified Rules create three, and they do not run together.
01
Tell the Board — without delay
Rule 7(2)(a). Not within 72 hours. On becoming aware, an intimation goes to the Data Protection Board describing the breach in the terms you have at that moment.
02
Tell the people — without delay
Rule 7(1). Each affected Data Principal, in their own right, told what happened, what it means for them and what to do. This is the duty most plans forget entirely.
03
Full particulars — 72 hours
Rule 7(2)(b). The detailed filing: facts, circumstances, mitigation, remedial measures and the intimations already given. Only this one has 72 hours attached.
“Without delay” is not “without undue delay”. The qualifier the GDPR uses is absent from Rule 7, and reading it in is how organisations end up explaining to the Board why the first two days were reasonable.
The trap
There is no severity threshold
No number of records makes a breach reportable, and no number makes one ignorable. Every personal data breach is notifiable.
01
Scale is not a gate
One record is a personal data breach. So is a spreadsheet emailed to the wrong person, and so is a laptop left in a taxi. The duty is the same in each case.
02
Harm is not a gate either
You do not get to decide it was minor, contained, or unlikely to affect anyone. Rule 7 has no materiality test to fail, so there is nothing to argue about afterwards.
03
What scale does change
How much work follows. Ten thousand people is ten thousand notifications, and that is a logistics problem, not a legal one. The obligation was already owed.
This is the single most expensive misunderstanding in Indian breach planning. Teams build a severity matrix, decide a breach falls below it, and stay quiet — which turns a reportable incident into a reportable incident plus a concealment.
The response
From “something has happened” to a filing
Declared by a person, not detected by us. From that moment the platform runs the clocks and drafts the paperwork.
1
Someone declares it
A member of staff records what they know and when they became aware. That timestamp is the one everything else is measured from, and it is written down before anybody has had time to become careful about it.
2
Scope comes from the registry
Naming the affected system pulls what it holds, which categories are involved and whether children’s or health data is among them. The hardest question of the first hour is answered from a map you already maintain.
3
Three obligations appear
Board intimation, Data Principal notification and the 72-hour filing, each with its own due time derived from the moment of awareness. Two of them show as needing action immediately, because they do.
4
Notices draft themselves
The intimation and the notice to affected people are built from what has been recorded, with the children’s and cross-border clauses added where they apply. Your DPO edits and approves rather than starting from an empty page.
5
Everything is already evidence
Each step is written to a timeline the database will not let anyone change or delete. When the Board asks what you did and when, the answer was recorded while you were doing it.
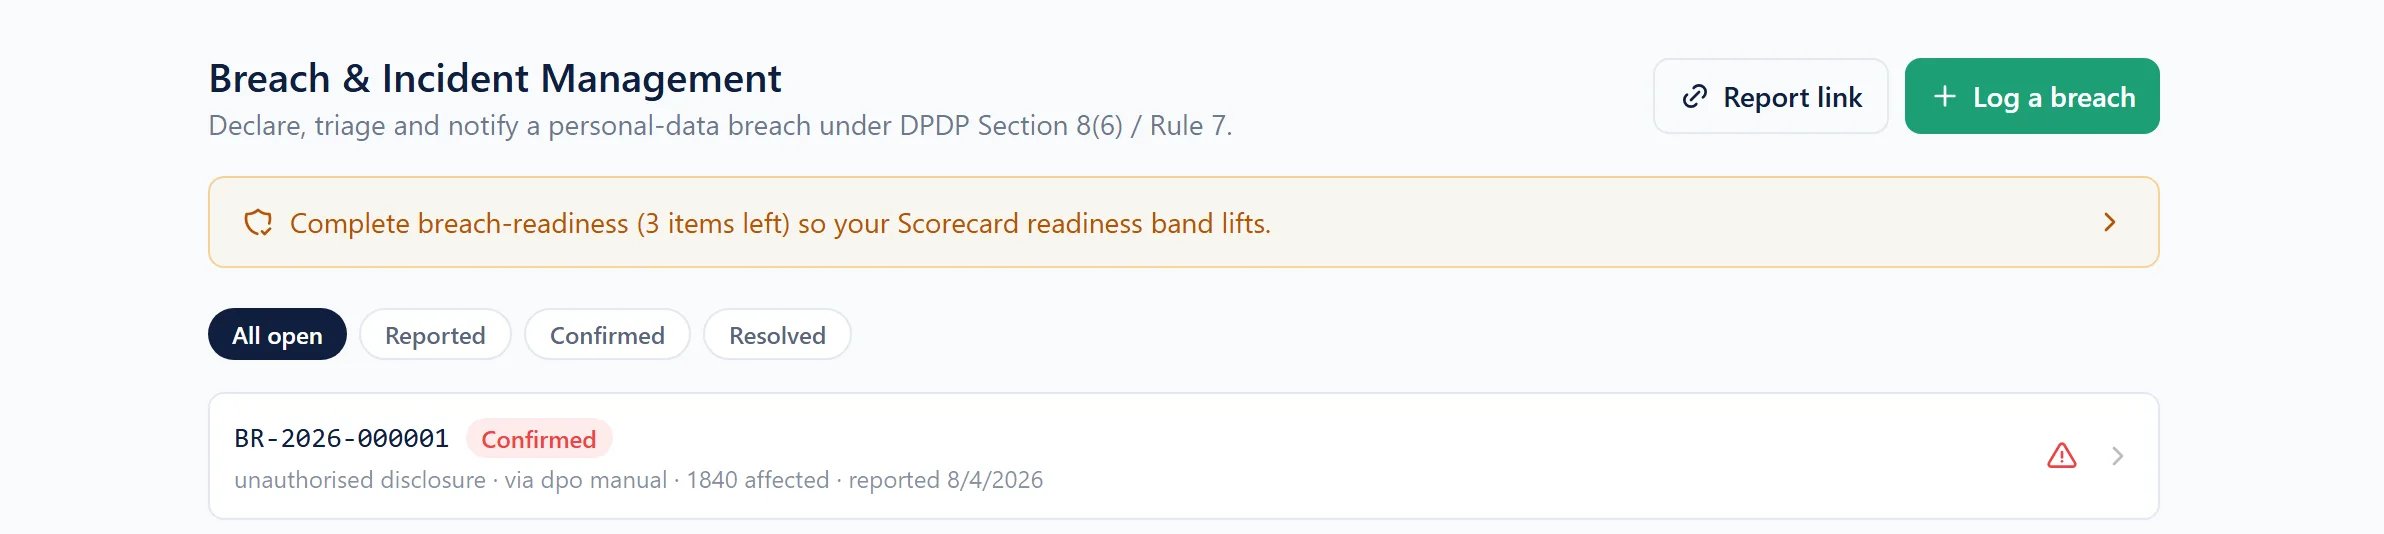
How the clock behaves
A without-delay duty is never “on track”
A countdown implies time you are entitled to spend. For two of these three duties, you are not entitled to any.
01
Due the moment you know
The Board intimation and the notice to affected people are due at the instant of awareness, so they never show green. They open amber, meaning act now.
02
Amber becomes red quickly
After a short internal window they turn red and stay there. That window is our own operational setting, not a grace period the Rules grant you, and it is labelled as ours.
03
Only the filing counts down
The 72-hour detailed filing is the one obligation with a genuine deadline to run against, and it is the only one shown as a countdown.
Rule 7(1)
The duty everyone forgets
Telling the Board is not the whole obligation. Each affected person has to be told directly, and told something useful.
01
What the notice has to carry
The nature and extent of the breach, when it happened, the likely consequences, what you have done about it, and safety steps the person can take themselves.
02
Who they contact
The business contact required by §8(9) has to be reachable and named. A notice that tells someone their data has gone and gives them nobody to ask is not a notice.
03
Reaching people you cannot email
Where contact details are missing or a category is too large to reach individually, a signed public notice page carries the same content and is recorded as the route used.
Nobody drafts their first breach notice well at two in the morning.
See the templates, the three clocks and a filing assembled from a live incident — on real screens, before you need them.
§33(2)
What you did is an express penalty factor
When the Board sets a penalty it must consider the mitigation you undertook and how promptly. That is written into the Act.
01
Promptness is measurable
The gap between becoming aware and acting is recorded to the minute, from a timestamp entered before anyone knew how the incident would turn out.
02
Mitigation is evidenced
What you did to contain it, in sequence, with who did it. A response you cannot produce a record of is one the Board cannot weigh in your favour.
03
The record cannot be tidied
The timeline is append-only at the database level. Nothing can be softened afterwards — which is precisely what makes it worth something as a defence.
Security failures carry the Act’s heaviest penalty at ₹250 Cr and breach-reporting failures ₹200 Cr. These are maxima set by the Board per contravention, not predictions — and §33(2) is the reason a documented response is worth having before you need it.
On the roadmap
What is coming, said plainly
Two things the earlier version of this page promised are not built. They are being built, and they are marked until they are.
Assisted severity assessment
Coming soon
A suggested grading from the categories and counts involved. It will never decide whether to report — there is no threshold, so that is not a judgement to automate.
Direct filing to the Board
Coming soon
Filing today is a prepared submission your DPO lodges. Direct filing waits on the Board publishing a machine interface, which is outside our control.
Bulk notification dispatch
Coming soon
Sending at the scale of a large breach needs messaging credentials. The notices, the routes and the record of who was told exist today.
Questions
About breach notification
Is it really 72 hours to report a data breach under DPDP?
Only for one of the three duties. Rule 7(2)(b) gives 72 hours for full particulars to the Data Protection Board. Rule 7(2)(a) requires an intimation to the Board without delay on becoming aware, and Rule 7(1) requires notifying each affected Data Principal without delay. Most DPDP breach guidance quotes the 72 hours and stops there, which is one line of three.
Our breach was small. Do we still have to report it?
Yes. Rule 7 sets no materiality threshold — no record count, no harm test, no severity gate. One person’s data disclosed to one wrong recipient is a personal data breach and is notifiable. This is where Indian practice differs sharply from what teams trained on other regimes expect, and it is the most common and most expensive mistake we see.
When exactly does the clock start?
On becoming aware — not on confirming, not on finishing the investigation, and not on deciding how bad it is. That is why the platform records awareness as a timestamp entered by the person who first knew, before the incident has been triaged. A clock that starts when the response is comfortable is not the clock the Rules describe.
Does the platform detect breaches for us?
No, and it is not sold as doing so. Breaches are declared by people — your staff, your IT provider, a vendor telling you they were compromised, sometimes a customer. Detection is what your security tooling does. What this handles is everything after: scoping it against your registry, running the three clocks, drafting the notices and holding the evidence.
Can we file to the Board directly from the platform?
Not yet, and not because we have not built it. The Board publishes no machine interface to file into, so anyone claiming one-click submission is describing something that does not exist. What the platform produces is the complete submission, drafted from the incident record, for your DPO to lodge and for the timeline to record as lodged.
What if we cannot contact everyone affected?
Rule 7(1) is a duty to notify each affected Data Principal, and where you hold contact details you use them. Where you do not, or where the affected group is too large to reach individually, a signed public notice carrying the same content is published and the route is recorded. What matters to the Board is that you notified, and that you can show how.
What compliance teams tell us
Real client quotes, attributed by role and sector — we never name a client.
DPDP, explained properly
DPDP in India: The Complete Guide to Data Protection Compliance, DPDP Guidelines and Automated Compliance Management (2026)
3 September 2026 · 35 min read DPDP Act
Healthcare Vendor Governance Under India’s DPDP Act: The Complete 2026–27 Compliance Framework
27 August 2026 · 32 min read DPDP Act
DPDP vs GDPR Compliance Tool: What’s Actually Different, and What a Tool Needs to Handle Both
26 August 2026 · 34 min readWorking across
Rehearse it before it happens.
A declared incident, scoped from a real registry, with three clocks running and a Board filing drafted from what was recorded — on live screens rather than slides.